> For the complete documentation index, see [llms.txt](https://qubitvpn.gitbook.io/qubitvpn-docs/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://qubitvpn.gitbook.io/qubitvpn-docs/extras/free-plesk-web-host-edition-license-for-premium-plan.md).
# FREE Plesk Web Host Edition License for Premium Plan
Instructions for QubitVPN Premium users on installing Plesk and activating it with the FREE Plesk Web Host Edition License (valued at $62.99/month) but we include it free of charge.
{% hint style="info" %}
**Please note, this only works on the QubitVPN *****Premium Plan*****.**
{% endhint %}
## What is Plesk?
Plesk is a Web Hosting Control Panel similar to cPanel (both are also owned by the same company, WebPros).
## How is QubitVPN able to offer this for free?
Our VPN servers run on the same servers as [Splicate’s Web Hosting Plans](https://www.splicate.com/web-hosting/). We get the keys for free and pass the savings onto you.
## How can I set up Plesk with QubitVPN and activate the key?
{% stepper %}
{% step %}
### Install Plesk
{% embed url="" %}
**If you are a beginner or just want default configuration, use this instead:**
* Installation instructions for Plesk for Linux: [Installing Plesk for Linux in One Click](https://docs.plesk.com/en-US/obsidian/deployment-guide/plesk-installation-and-upgrade-on-single-server/1click-plesk-installation/installing-plesk-for-linux-in-one-click.76444/).
* Installation instructions for Plesk for Windows: [Installing Plesk for Windows in One Click](https://docs.plesk.com/en-US/obsidian/deployment-guide/plesk-installation-and-upgrade-on-single-server/1click-plesk-installation/installing-plesk-for-windows-in-one-click.76448/).
{% endstep %}
{% step %}
### Set up WireGuard
1. [Download NetBird (QubitVPN Client)](/qubitvpn-docs/how-to-use/download-netbird-qubitvpn-client.md)
2. Open the [Plesk ports](https://docs.plesk.com/en-US/obsidian/administrator-guide/plesk-administration/ports-used-by-plesk.64950/) on your computer/server > [Allow Incoming Port Connection](/qubitvpn-docs/how-to-use/allow-incoming-port-connection.md)
3. Tunnel the [Plesk ports](https://docs.plesk.com/en-US/obsidian/administrator-guide/plesk-administration/ports-used-by-plesk.64950/) using the [Port Forward Manager](/qubitvpn-docs/how-to-use/how-to-use.md#setup-port-forwarding-tunneling-only-available-from-the-standard-plan-and-higher-tiers).
{% endstep %}
{% step %}
### Reconfigure Plesk
Reconfigure Plesk to use the WireGuard IP
{% tabs %}
{% tab title="Linux" %}
```bash
plesk repair all -y
```
{% endtab %}
{% tab title="Windows" %}
Run Plesk Repair Utility (usually in C:\Program Files (x86)\Plesk\admin\bin)
Run CMD and then:
```batch
cd C:\Program Files (x86)\Plesk\admin\bin
plesk repair all -y
```
{% endtab %}
{% endtabs %}
{% endstep %}
{% step %}
### Log into Plesk
1.
2. Use your SSH username and password
You may also log-in with a one-time link with this command:plesk login
{% endstep %}
{% step %}
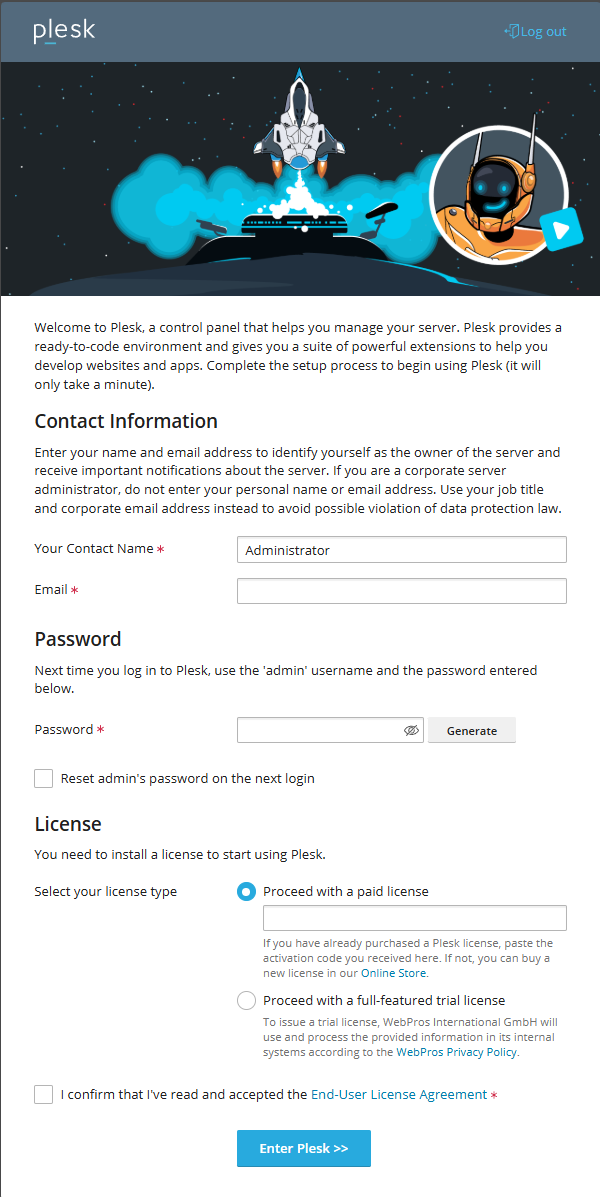
### Enter your Email and create a Password
{% endstep %}
{% step %}
### Enter License Key
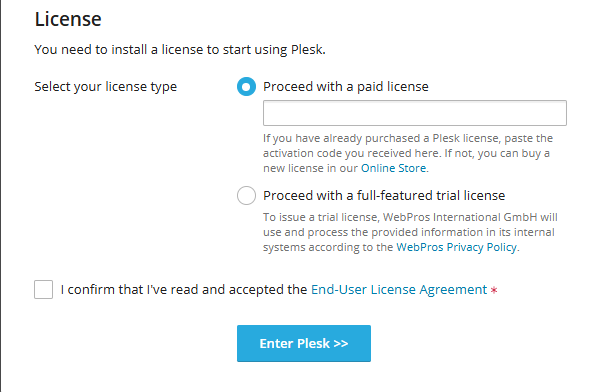
Select "Proceed with a paid license" and enter the license key that was sent to your email after server provisioning. If the email doesn't contain a key, please contact us by email[^1] or by live chat (on our [website](https://qubitvpn.com/)), to claim your key.
{% endstep %}
{% step %}
### Add VPN IP as a Trusted IP (to avoid issues later on)
Go to (change "your-ip" with your actual IP).
If this doesn't work, then follow the steps below, if it does, then skip to step 3.
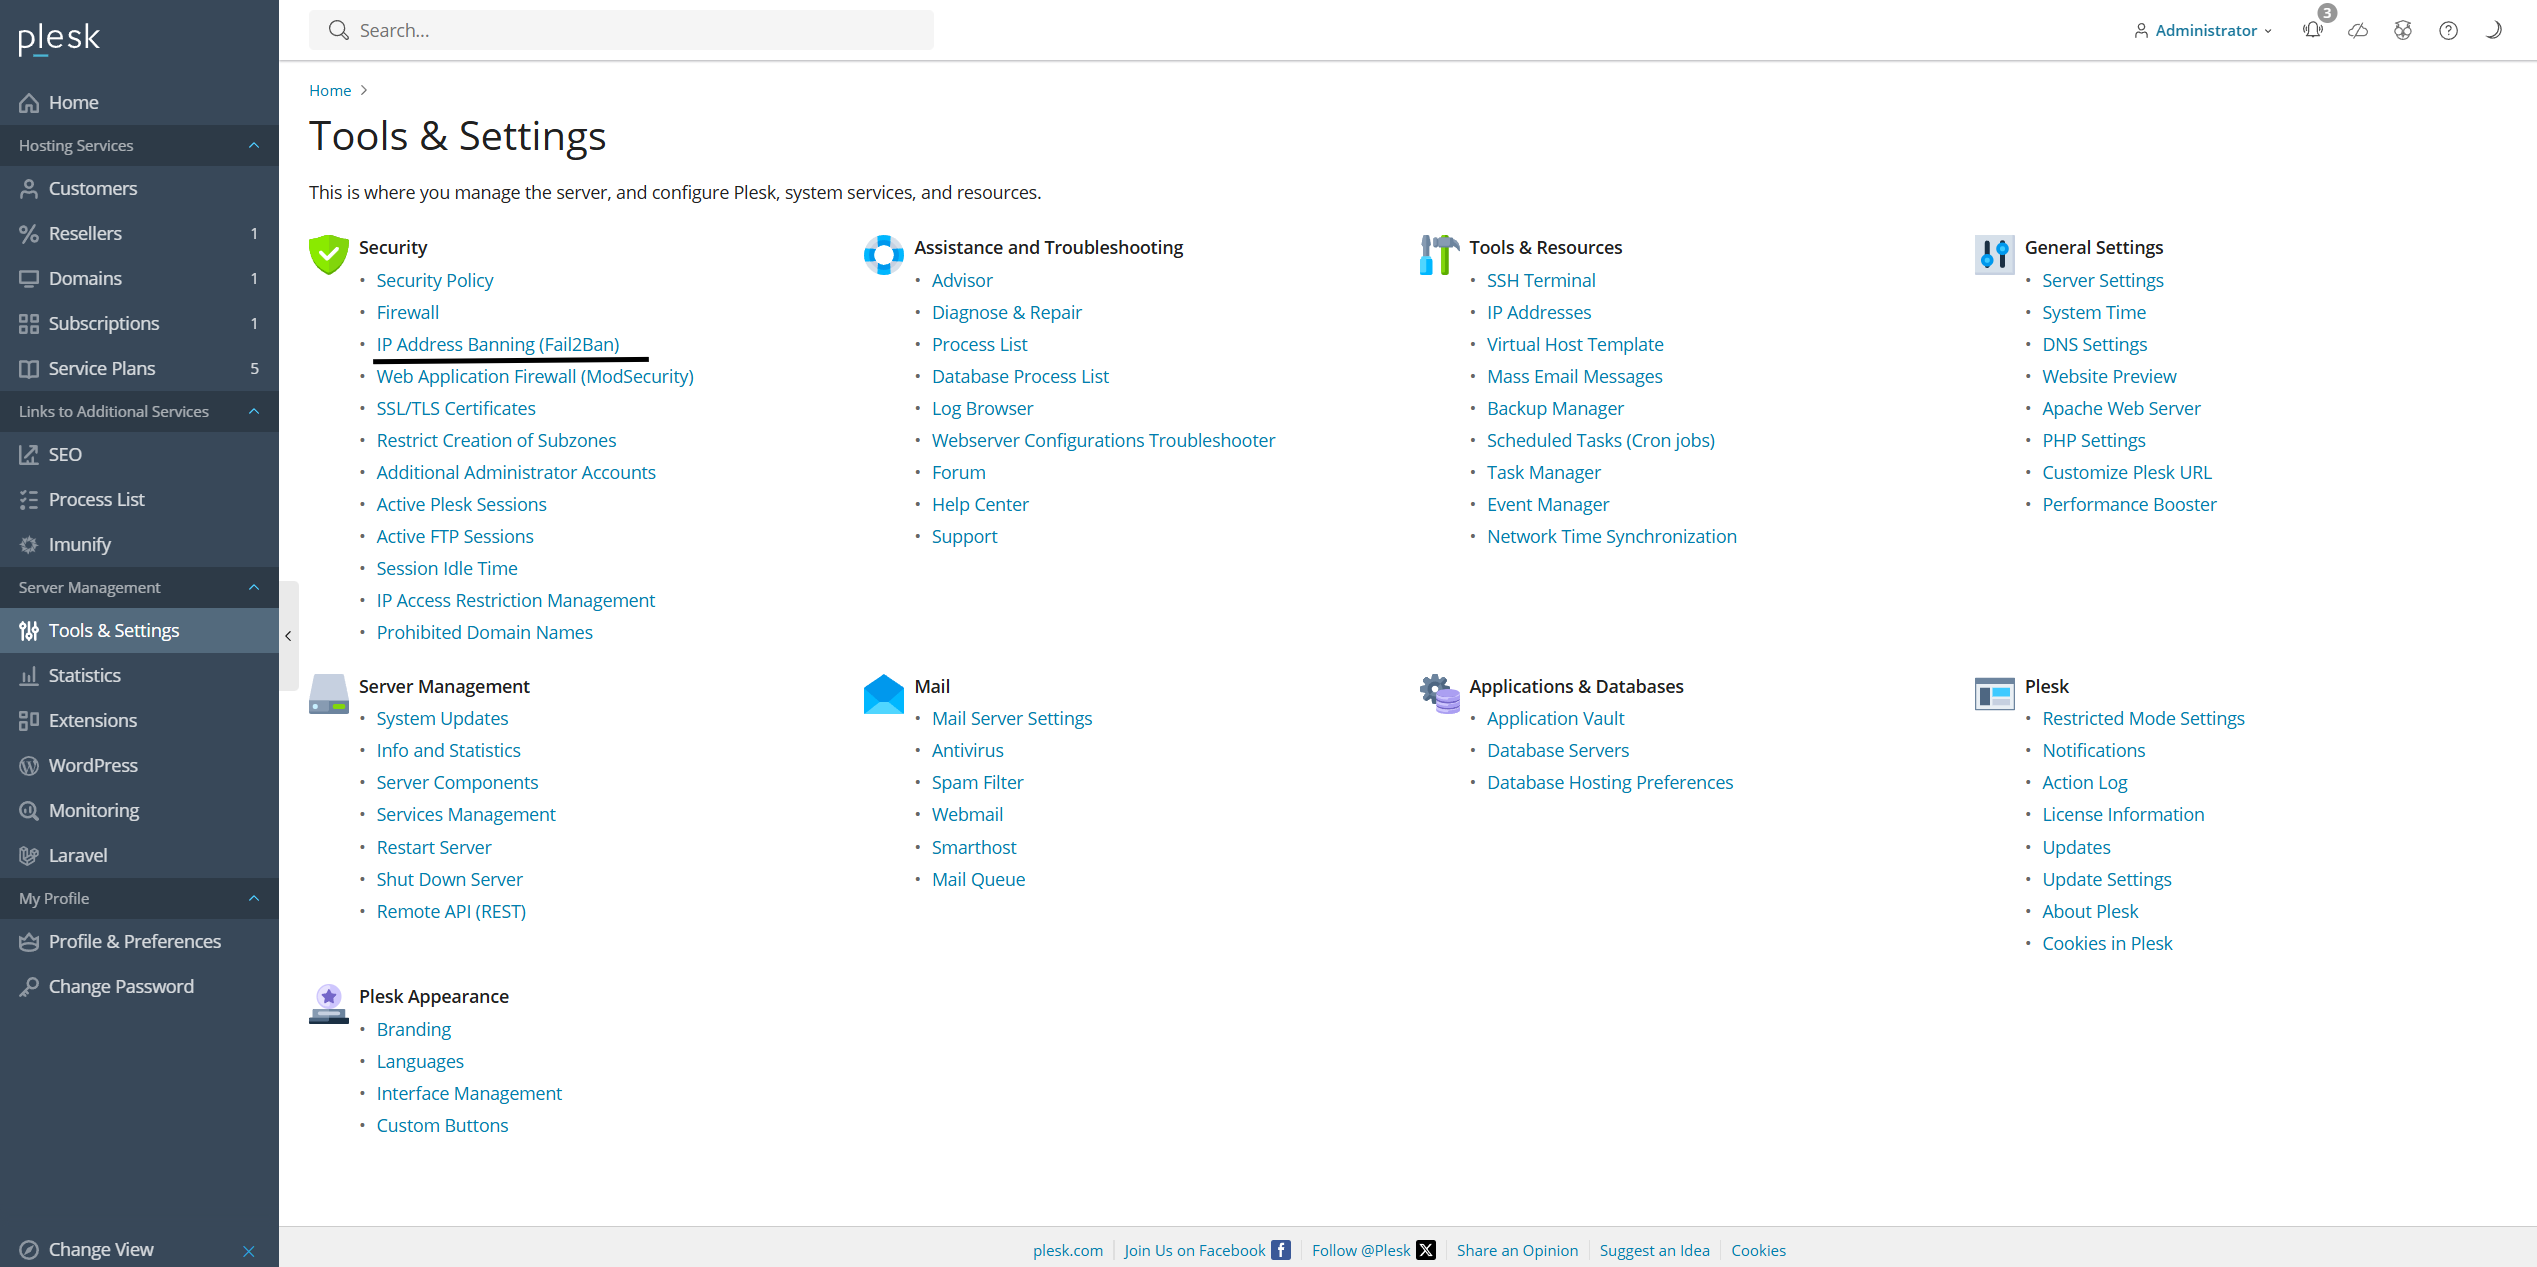
1. Go to Tools & Settings > IP Address Banning (Fail2Ban)
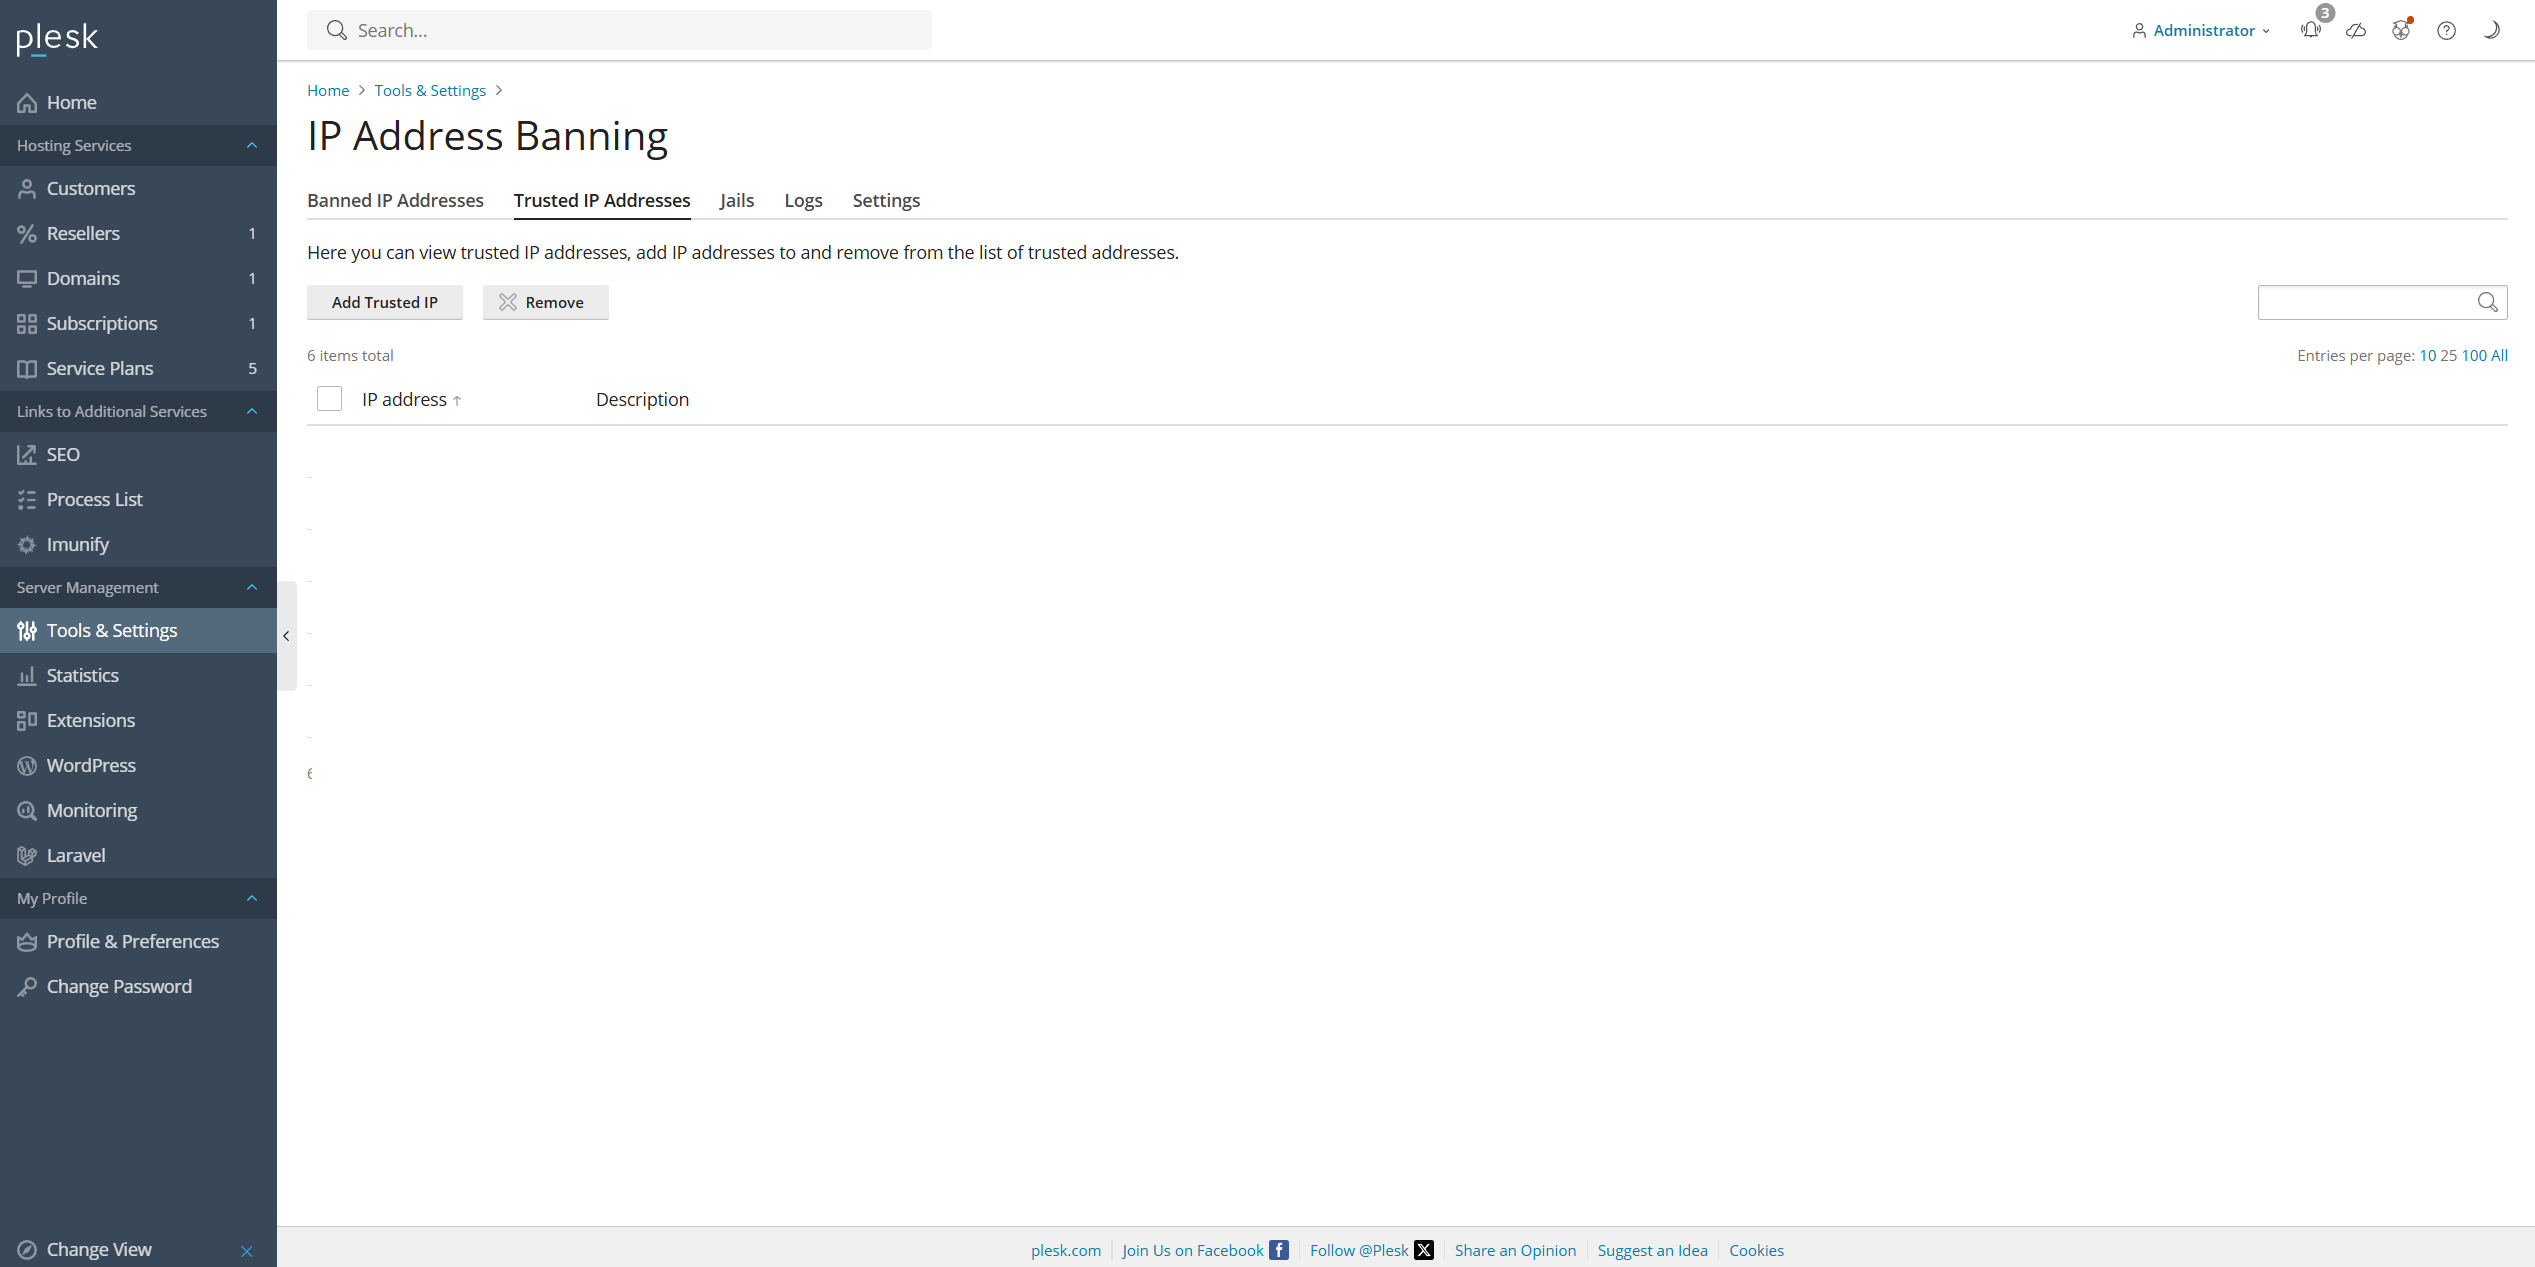
2. Click on "Trusted IP Addresses" on top
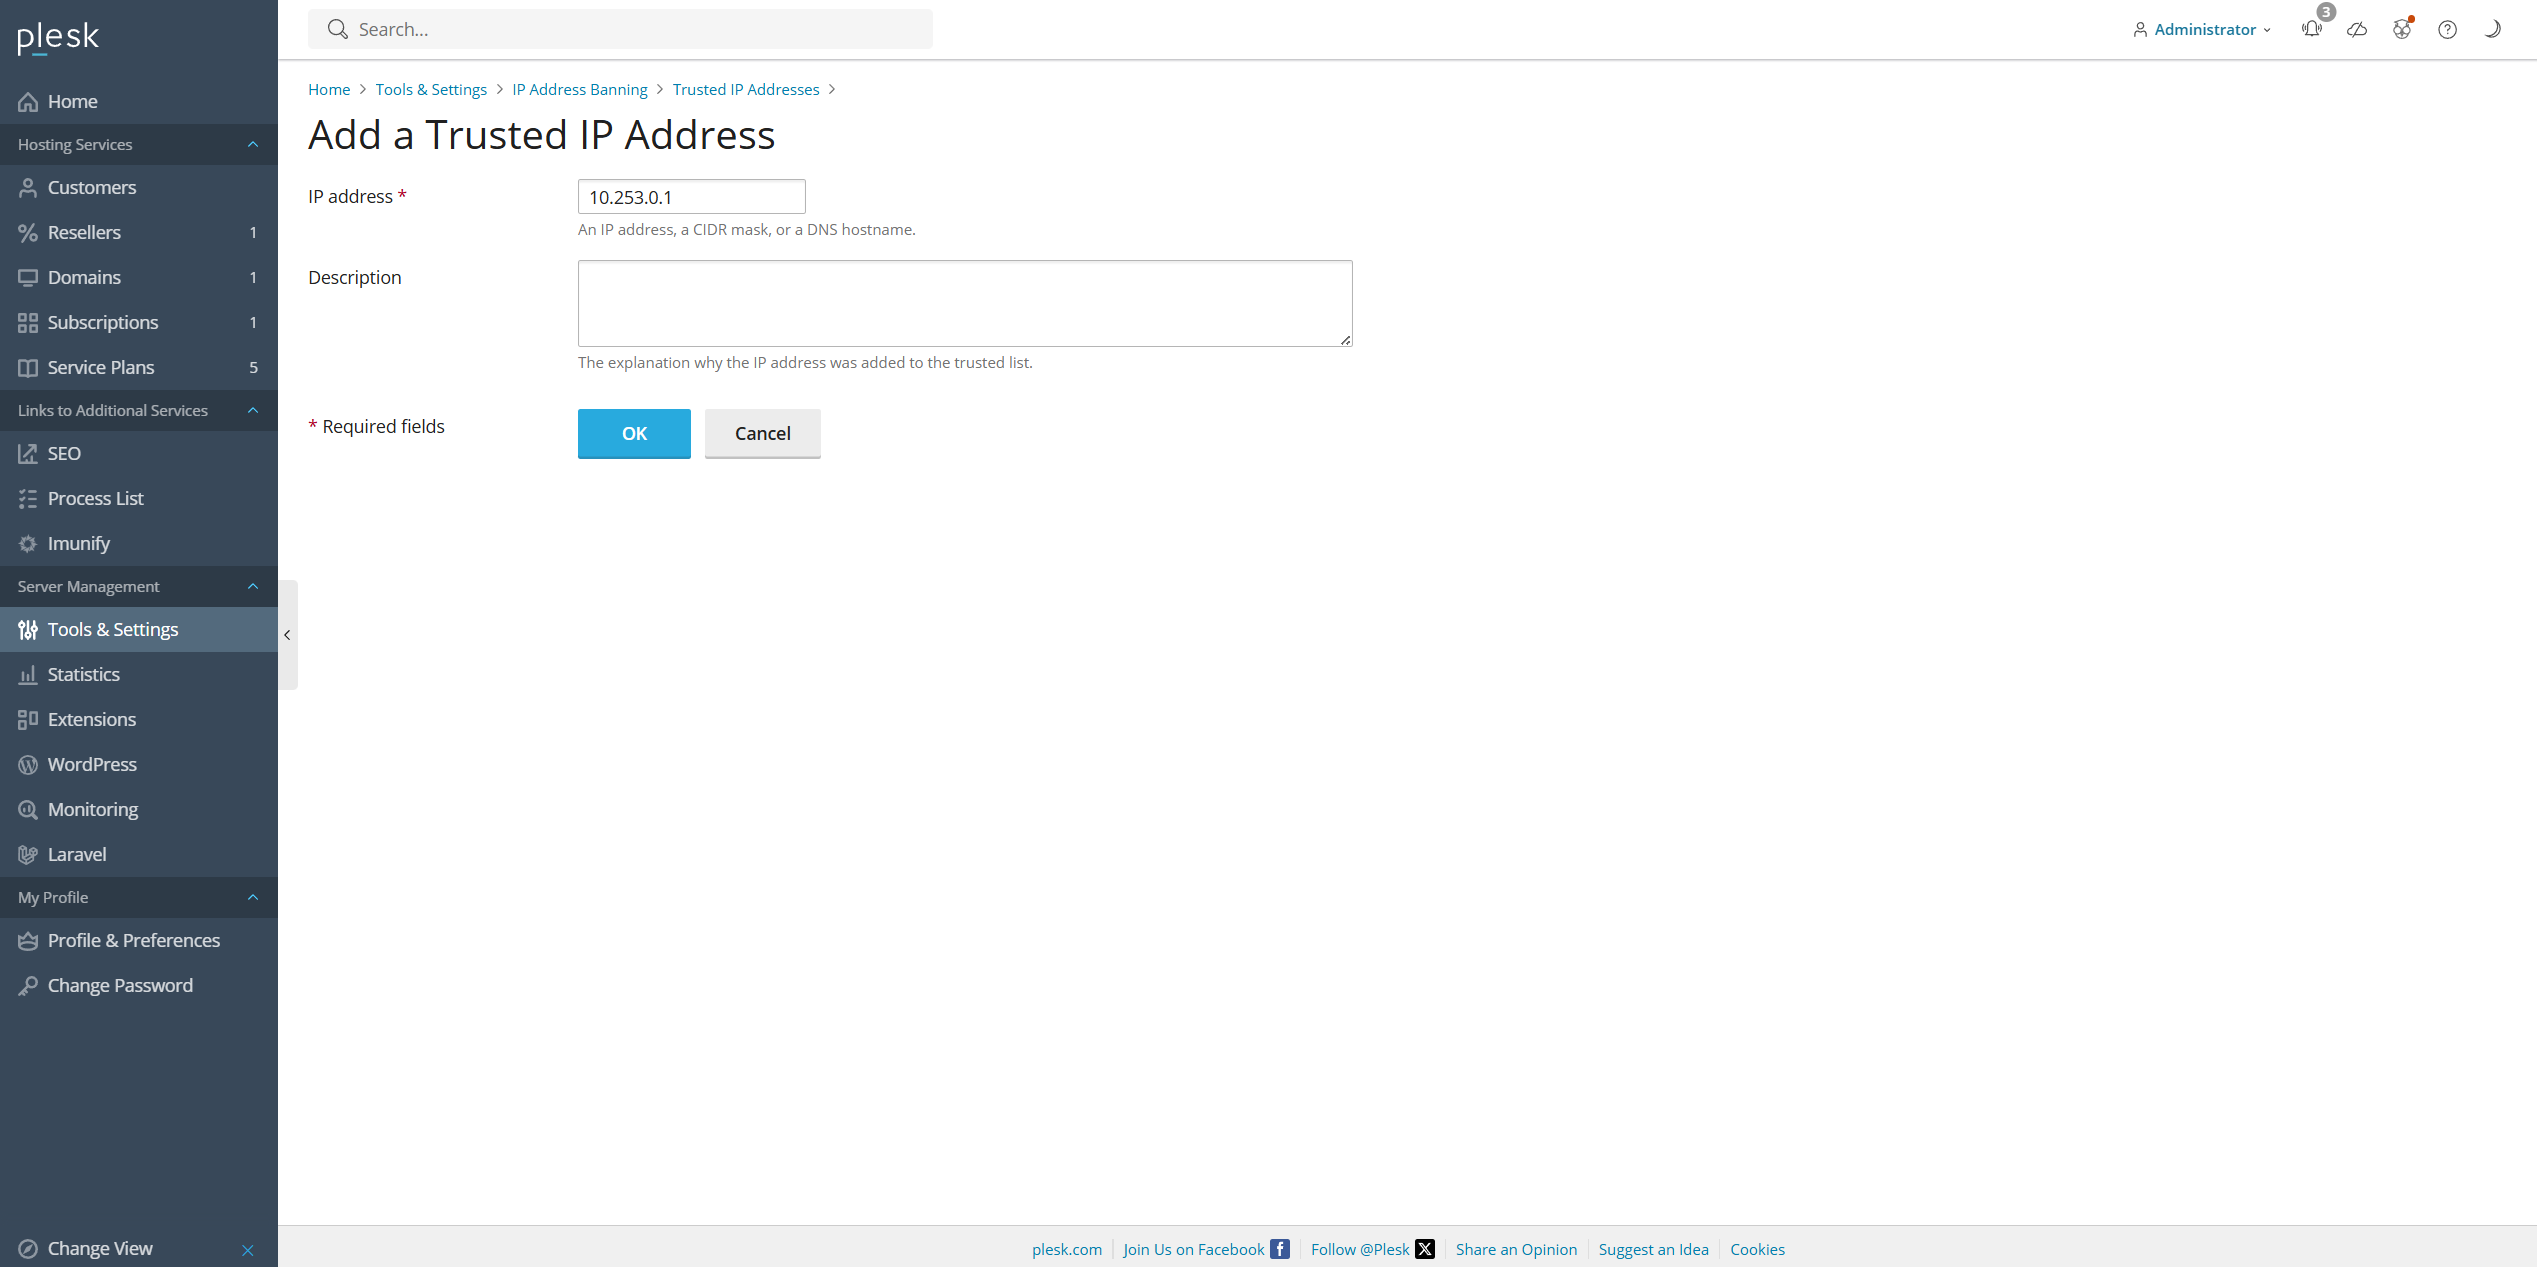
3. Click on "Add Trusted IP" and add your WireGuard VPN Server IP (usually 10.253.0.1) and click "OK" when you're done.
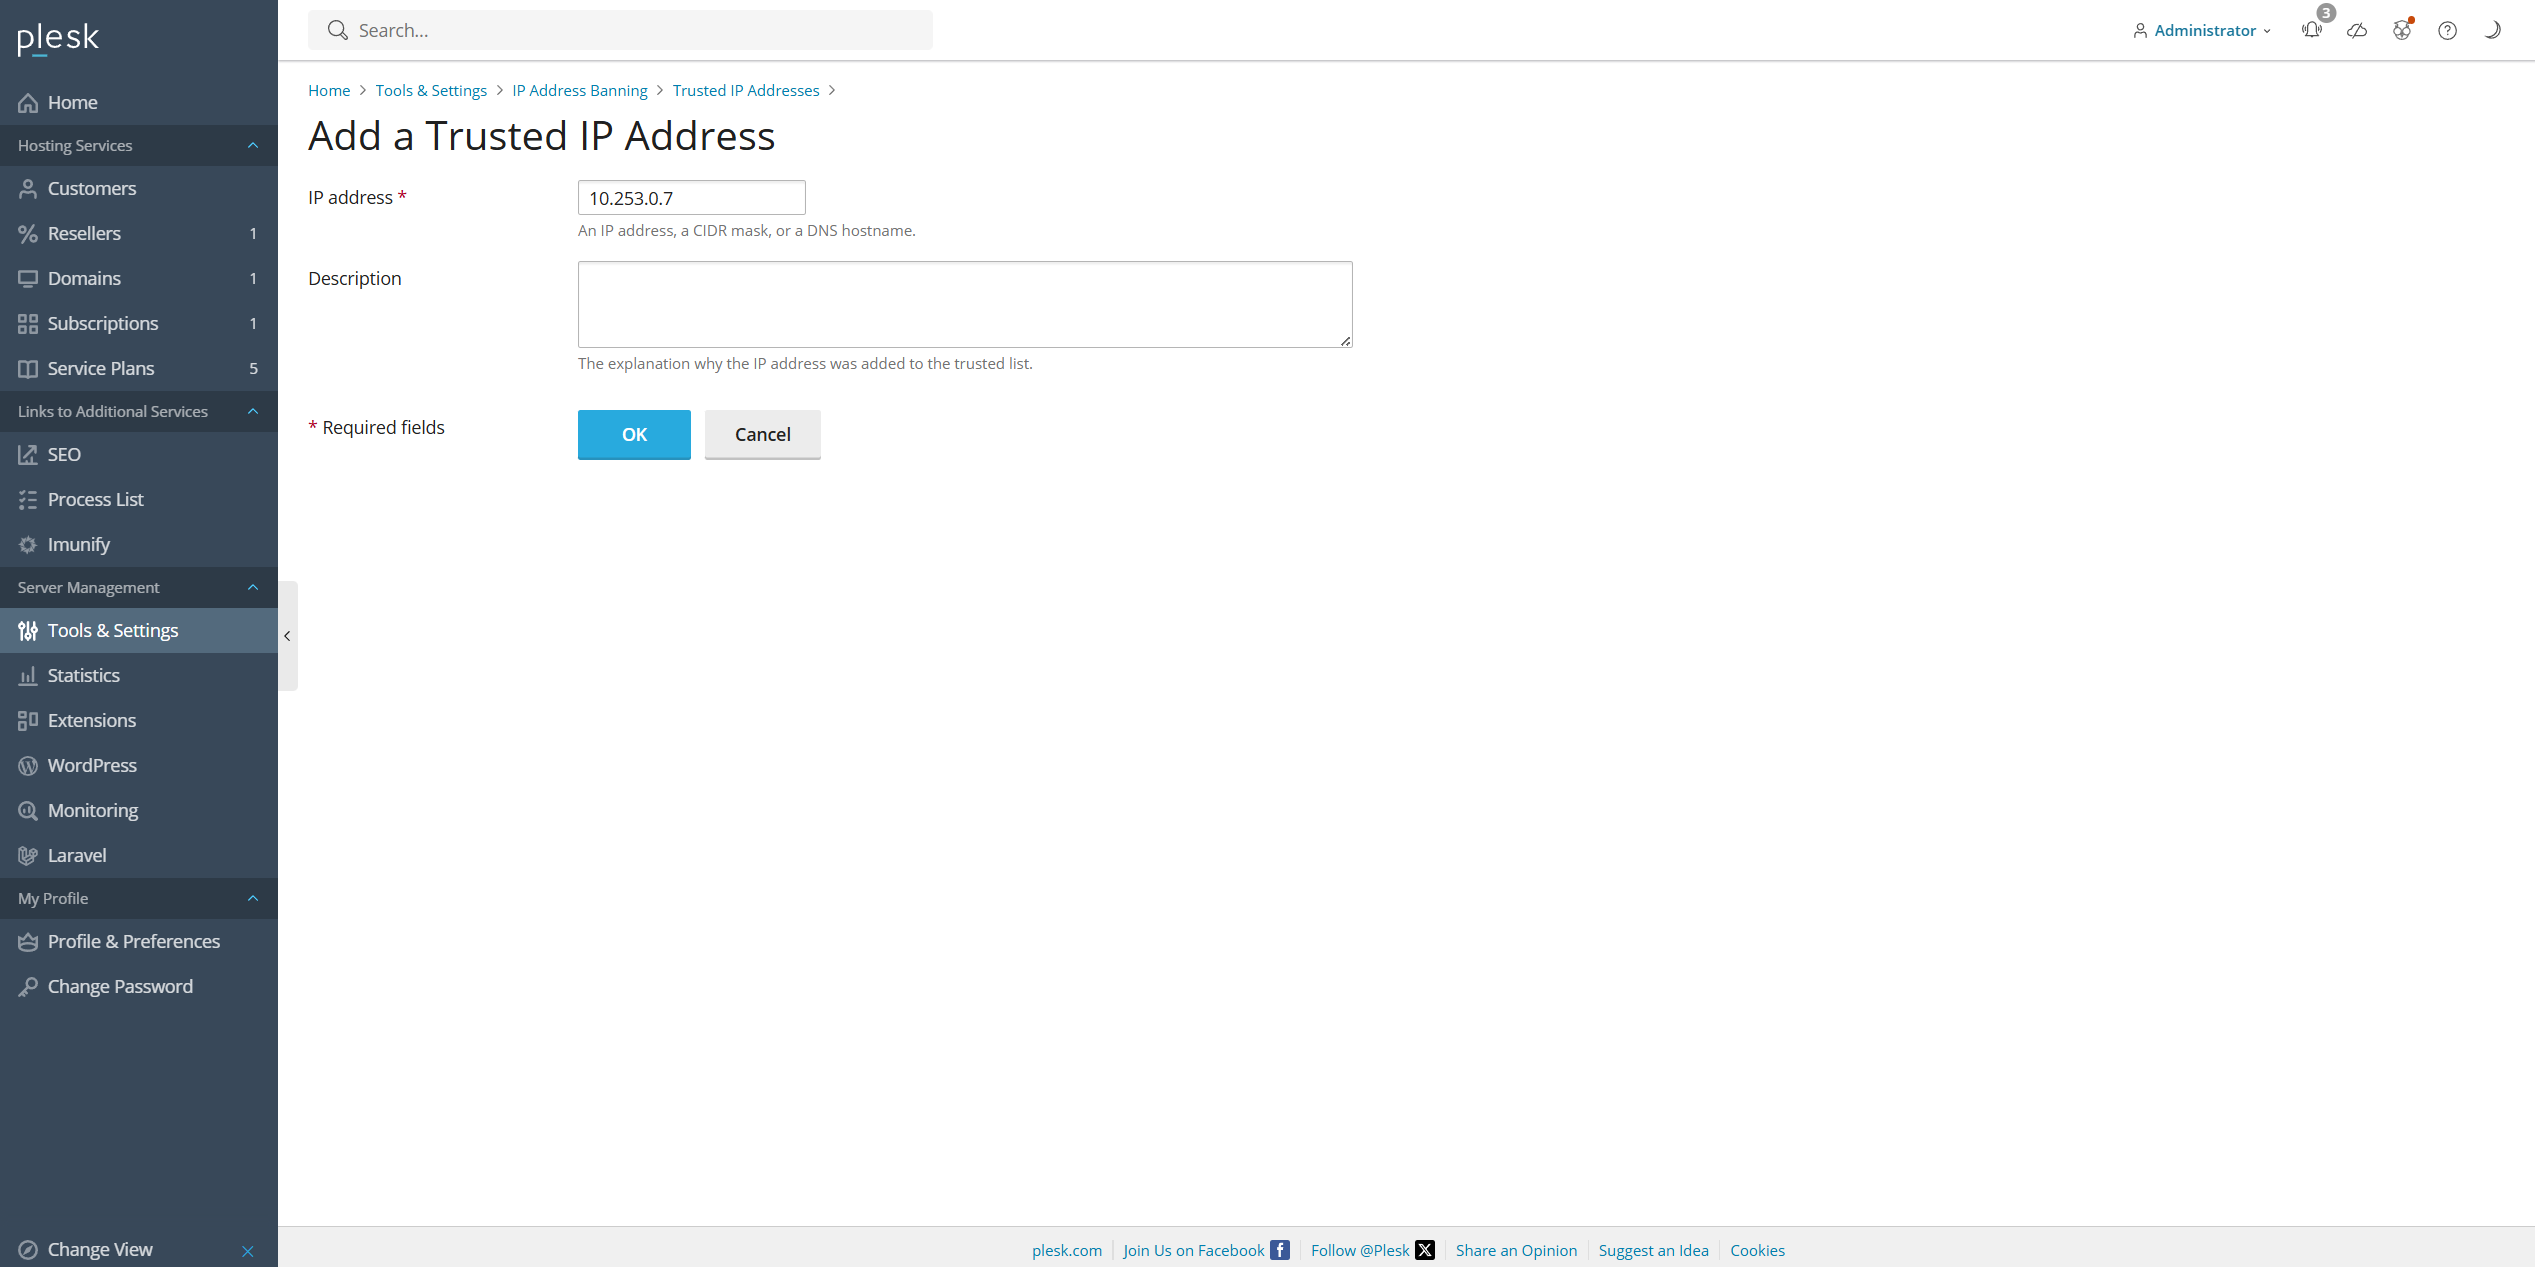
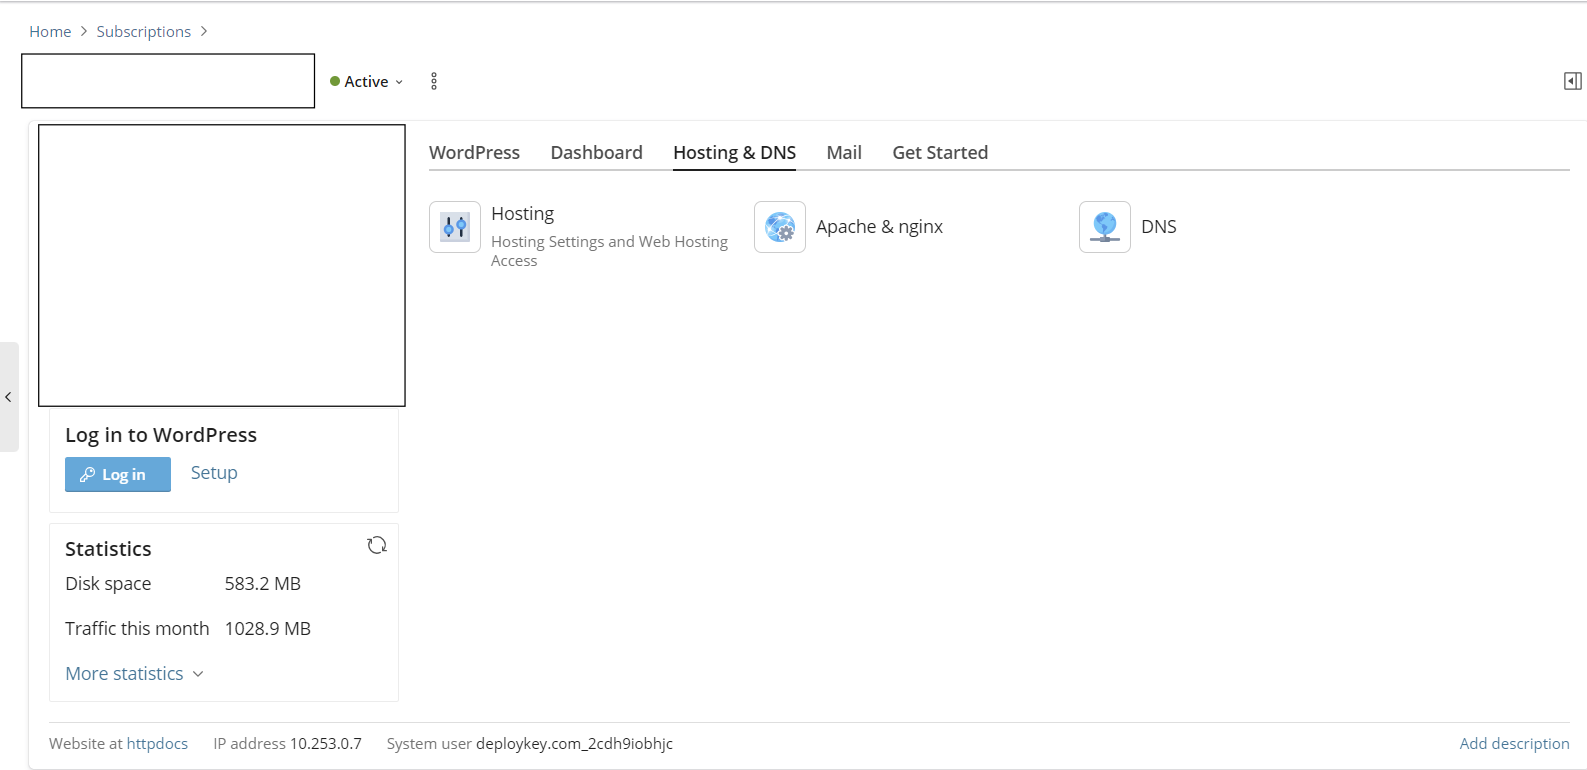
4. Click on "Add Trusted IP" again and add your Tunnel Config IP (e.g. 10.253.0.7) and click "OK" when you're done.
{% endstep %}
{% step %}
### IP Tracking and Security
{% tabs fullWidth="false" %}
{% tab title="How to choose" %}
There are 2 ways to track real IPs.
You may use *X-Forwarded-For* or *CF-Connecting-IP* (Cloudflare) within the website. This only works on some websites and may require a plugin. You can accomplish this on WordPress using a plugin like Solid Security.
Or:
You may do it for the whole website through settings. This will work on most if not all website types and does not require a plugin in most cases.
Please choose the tab that fits with your preferred method.
{% endtab %}
{% tab title="Using X-Forwarded-For or CF-Connecting-IP" %}
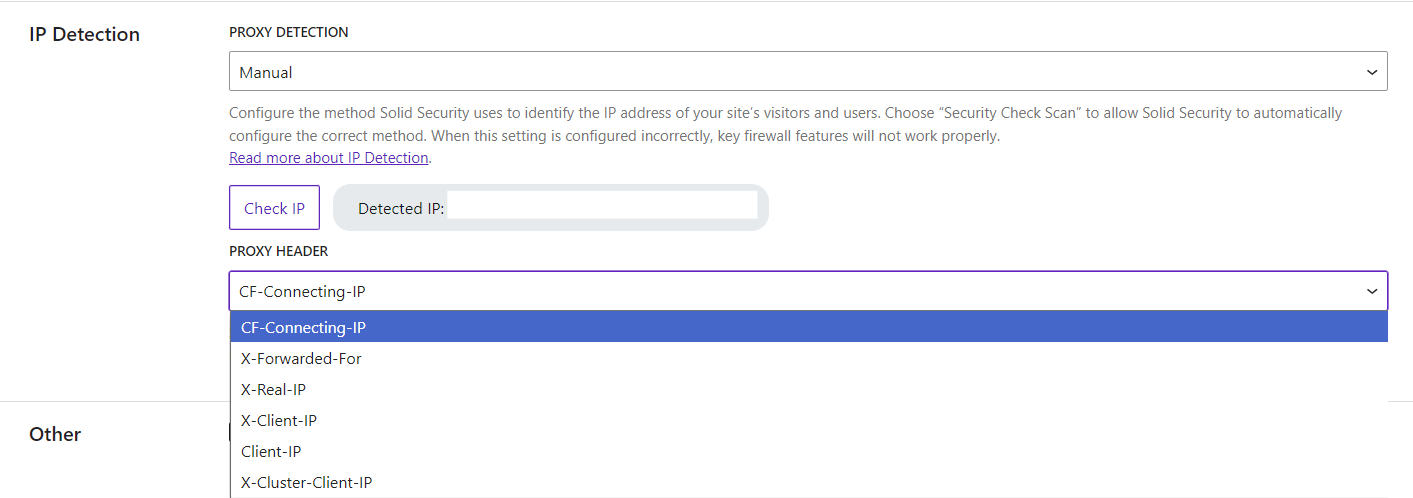
For website security (like a WordPress security plugin), use X-Forwarded-For (XFF) or CF-Connecting-IP. *Do **NOT** use X-Real-IP, X-Client-IP, Client-IP, or X-Cluster-Client-IP.*
*Our personal favorite security plugin for WordPress is Solid Security. (We are not in any way affiliated or sponsored by Solid Security)*
How to set this up in [Solid Security](https://wordpress.org/plugins/better-wp-security/):
1. Install [Solid Security](https://wordpress.org/plugins/better-wp-security/)
2. Go to Solid Security > Settings > Global Settings
3. Scroll Down to "IP Detection"
4. Select CF-Connecting-IP if using Cloudflare, if not, select X-Forwarded-For
5. Click "Check IP" and make sure that is your own IP (the IP you're accessing the website from). This should be the IPv6 or IPv4 from [here](https://whatismyipaddress.com/). If this shows "10.253.0.1" or something similar, you did something wrong. Please go back through the steps to see where you made an error.
{% hint style="success" %}
If this shows your personal/work or VPN (if using one) IP, then you are now successfully tracking real IPs.
{% endhint %}
{% endtab %}
{% tab title="Whole Website" %}
{% stepper %}
{% step %}
### Go to your website > Hosting & DNS > Apache & nginx
{% endstep %}
{% step %}
### Add these:
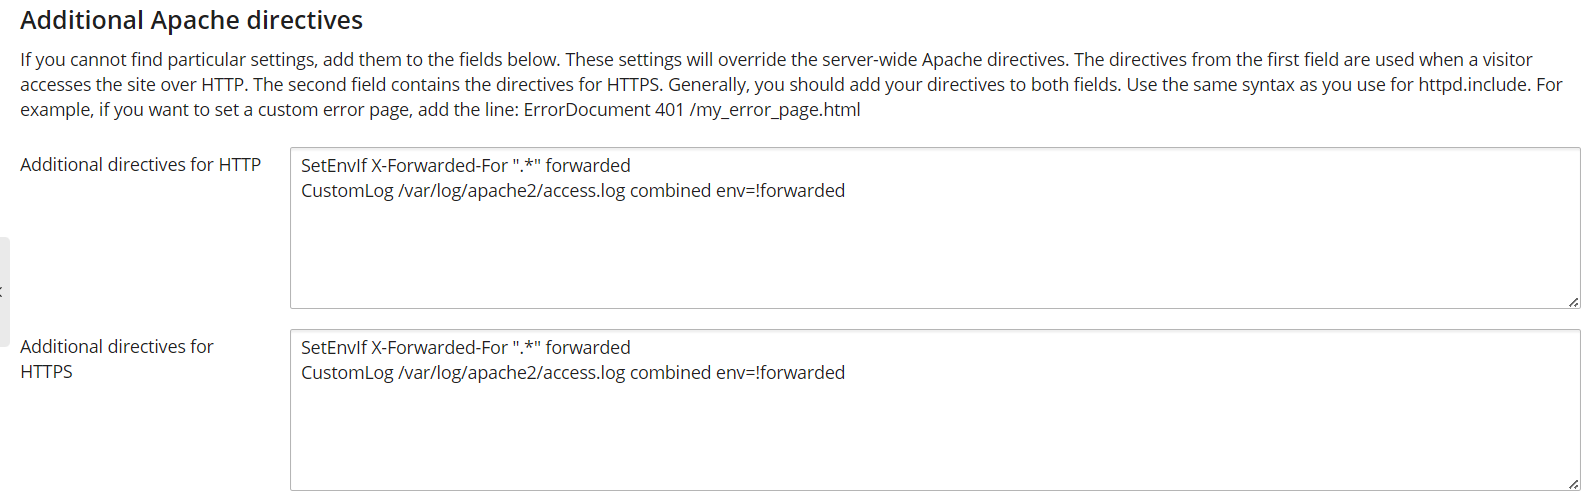
In the "Additional directives for HTTP" and "Additional directives for HTTPS" boxes, enter:
```
SetEnvIf X-Forwarded-For ".*" forwarded
CustomLog /var/log/apache2/access.log combined env=!forwarded
```
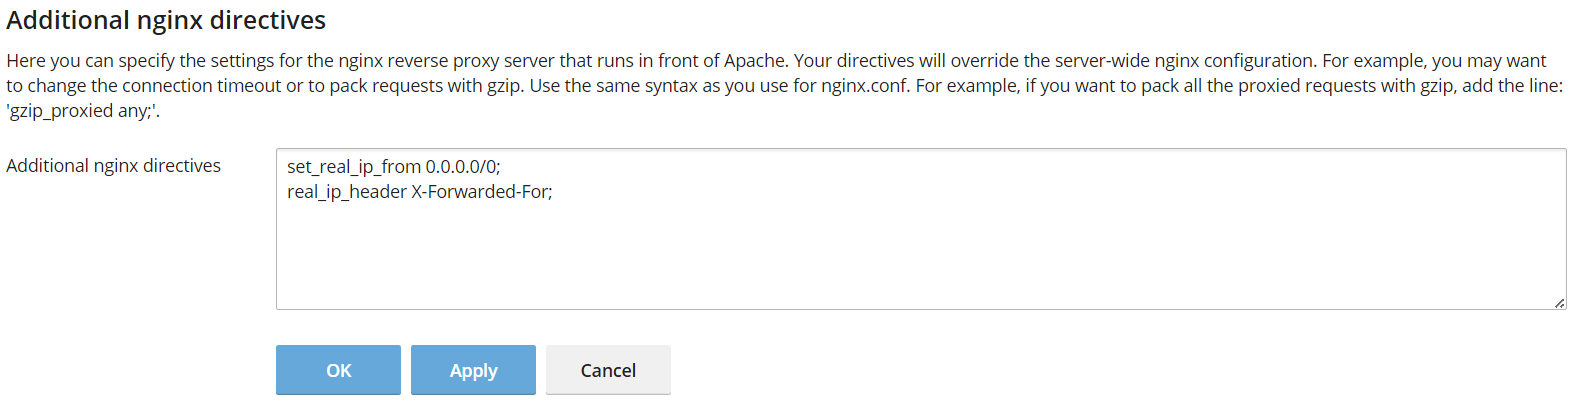
In the "Additional nginx directives" box, enter:
```
set_real_ip_from 0.0.0.0/0;
real_ip_header X-Forwarded-For;
```
{% endstep %}
{% step %}
### Success!
{% hint style="success" %}
Your personal/work or VPN (if using one) IP should now be tracked instead of the VPN Server IP.
{% endhint %}
{% endstep %}
{% endstepper %}
{% endtab %}
{% endtabs %}
{% endstep %}
{% step %}
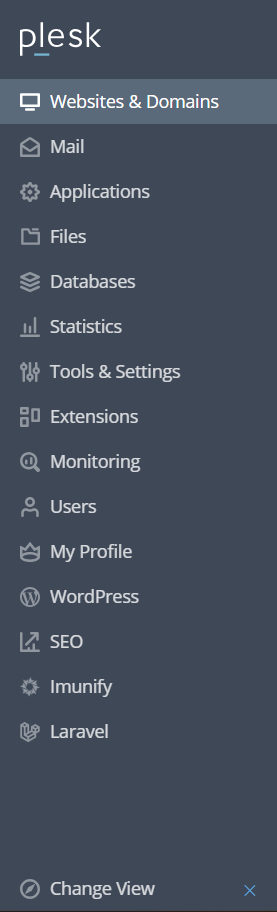
### Declutter with Power User View (Optional)
Best for developers and web agencies. If you aren't planning to resell and want to declutter all the menu options, follow the steps below:
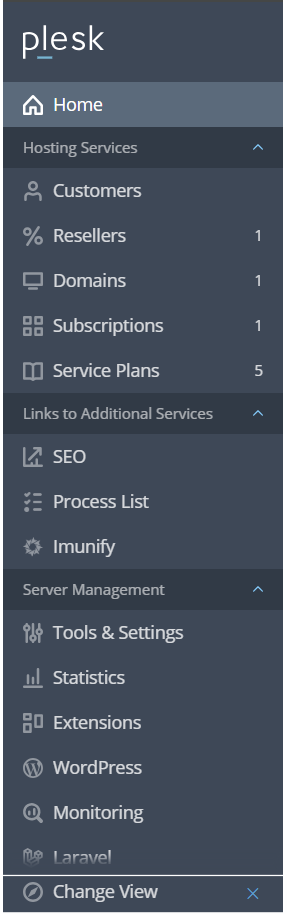
1. Click on "Change View" at the bottom of the your left hand menu
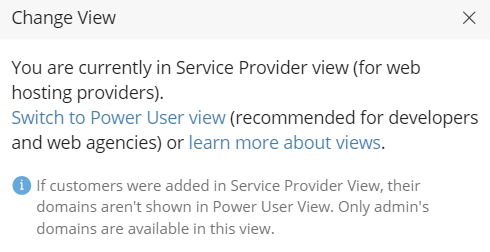
2. Click "Switch to Power User view"
3. Now you have a much simpler, decluttered menu!
{% endstep %}
{% endstepper %}
[^1]: